Is Your Website Legal Under India's DPDP Act?
If you run a website in India, big changes have arrived.
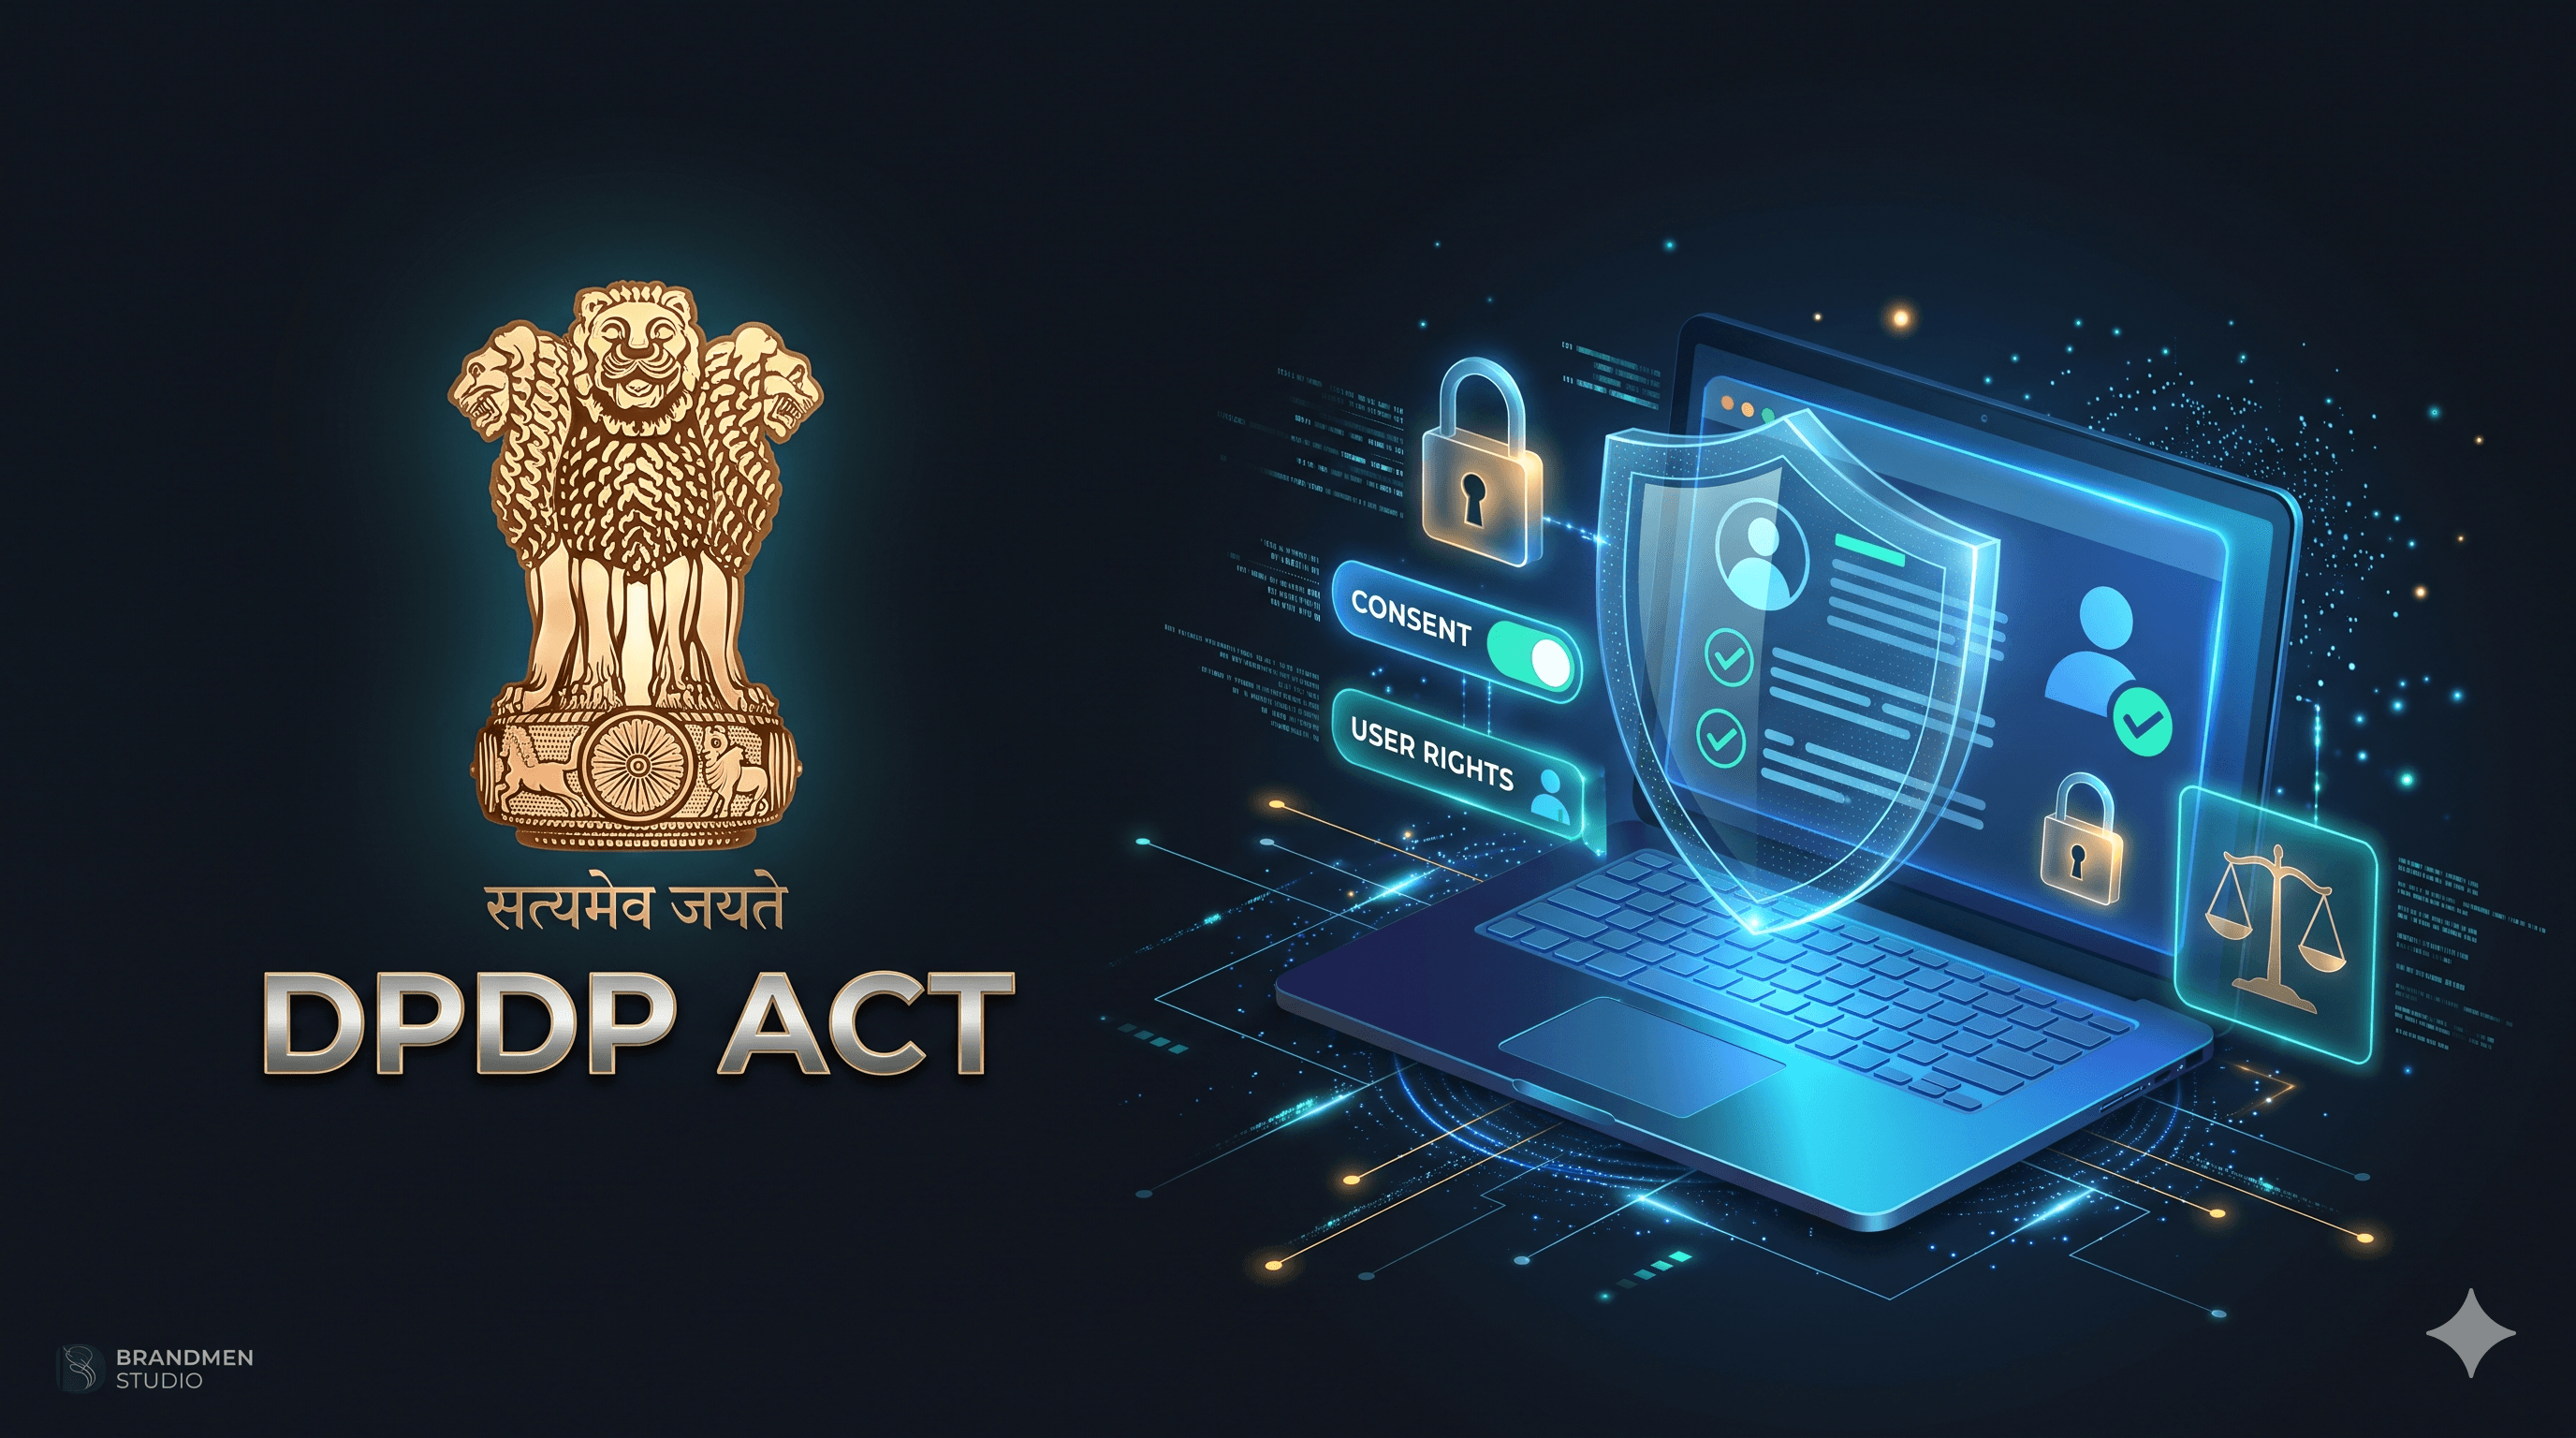
The Government of India passed the Digital Personal Data Protection (DPDP) Act, and the rules apply to everyone.
Whether you run a local clinic, an e-commerce store, a consulting firm, or an educational academy, your website collects customer data every single day.
Non-compliance carries penalties that can climb up to 250 Crore Rupees for major data security failures and privacy violations.
You do not need a law degree to fix this. At BrandMen Studio, we break down complex tech into simple action steps.
Here is everything you need to know and change across your website experience to stay safe, transparent, and fully compliant.
1. Stop Bundled Consents and Pre-Ticked Checkboxes*
Many websites have checkboxes that say: "I agree to the Terms, Privacy Policy, and to receive promotional WhatsApp messages," with the box already ticked.
Under the DPDP Act, this is illegal.
- No Pre-Ticked Boxes: The box must start empty. The visitor must physically click it themselves.
- Unbundled Consent: You cannot club terms and marketing together. You need separate checkboxes: one for the service agreement and an optional one for marketing updates.
- Clear Language: Do not hide consents inside complicated legal jargon. State plainly what data you collect and why.
2. Make Consent Withdrawal as Easy as Giving It
If a user clicks a button to sign up or share their phone number, leaving should be just as effortless.
- One-Click Opt-Out: Add an easy "Unsubscribe" or "Manage Consent" link in user profiles, account dashboards, or website footers.
- Real-Time Revocation: When someone withdraws consent, your backend database and CRM must immediately update and stop processing their data for that purpose.
3. Multilingual Notices and Plain-Language Summaries
Most Indians browse the web in regional languages. The DPDP Act emphasizes that users must understand what they are signing up for.
- Language Switcher on Privacy Notices: Provide clear consent notices not just in English, but in scheduled regional languages like Telugu, Hindi, Odia, or Tamil depending on your primary user base.
- Bite-Sized Summaries: Place a short, easy-to-read 3-point summary right beside contact forms and signup boxes instead of forcing visitors to read a 20-page legal document.
4. Total Overhaul of Contact Forms and Lead Generation
Many landing pages ask for unnecessary information like full date of birth, home address, and gender for a simple quote.
- Data Minimization: Only ask for what is strictly needed to deliver the service. If you only need a phone number to schedule a call, do not ask for five extra fields.
- Just-in-Time Notice: Right below the submit button, display a one-line note stating: "We will only use this number to call you back regarding your inquiry. Read our Privacy Notice."
5. Cookie Banners and Tracking Scripts
If your website uses Google Analytics, Meta Pixel, Hotjar, or retargeting ad tags, you are tracking personal behavioral data.
- Active Cookie Consent: You cannot drop tracking cookies before the user gives permission.
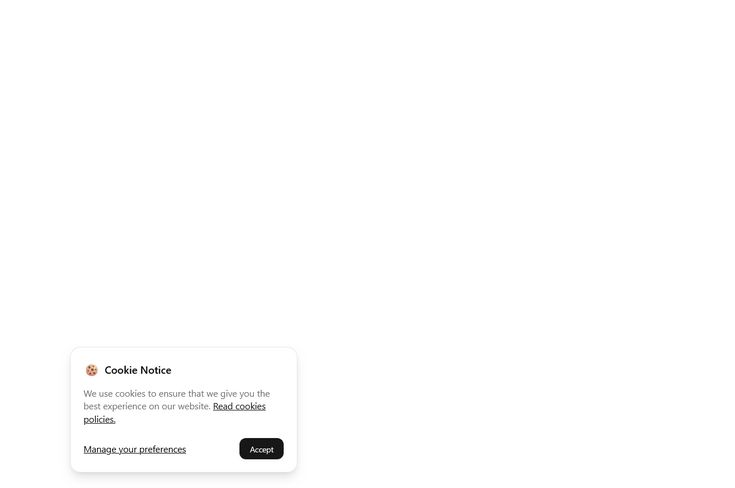
- Categorized Cookie Center: Offer clear options for Essential, Analytics, and Advertising cookies. Allow visitors to accept all, reject non-essential cookies, or customize preferences.
- No Dark Patterns: Both "Accept" and "Decline" buttons must have equal visual prominence. Do not hide the reject button in low-contrast gray text.
6. Self-Service User Rights Dashboard (Data Principal Rights)
Indian citizens now have statutory rights over their digital data. Your website must provide a simple way for users to exercise them:
- Right to Access: Users can request a copy of the data you hold about them.
- Right to Correction: Users must be able to update incorrect details easily.
- Right to Erasure: A simple "Delete My Account & Data" option should wipe out their profile from active records once legal obligations are cleared.
- Right to Nominate: Users have the right to nominate someone who can manage or delete their data in case of death or incapacity.
7. Mandatory Grievance Officer and Contact Details
Every company acting as a data fiduciary must provide a clear grievance redressal route.
- Publish Officer Information: Display the name, official email address, and physical contact details of your Data Grievance Officer directly on your Privacy Policy and website footer.
- Grievance Form or Ticket System: Provide a simple web form to log privacy complaints, along with clear service level response times.
8. Strict Protections for Children's Data
If your website offers courses, games, coaching, or services accessed by minors (under 18 years), extra guardrails are mandatory.
- Verifiable Parental Consent: You must verify parental or guardian approval before collecting data from children.
- No Targeted Ads or Behavioral Profiling: Running behavioral tracking or personalized ads directed at children is strictly prohibited.
9. Technical Security, Hosting, and Breach Protocols
Compliance is not just about words on a page; it is about how securely your website runs behind the scenes.
- Encryption Everywhere: Ensure HTTPS (SSL/TLS) is enforced across every single page and database connection.
- Clean Third-Party Integrations: Review all WordPress plugins, external APIs, and script tags. If a plugin leaks customer data, your business remains legally responsible.
- Breach Reporting Readiness: Set up automated server logging and monitoring so you can detect, stop, and report any data breach to authorities and affected users without delay.
The Bottom Line
DPDP Act compliance is not just about avoiding legal trouble.
When your website respects user choices, avoids spam tricks, and keeps customer information secure, it builds immediate trust.
At BrandMen Studio, we build modern websites and digital platforms that pair high-converting user experience with rock-solid data privacy.
Audit your forms, check your cookies, update your notices, and turn your compliance into a real competitive advantage.
Published: October 25, 2026
Last updated: 2026-05-27
Sources